Editorial Team
5 min read
Israeli incident-response firm Profero says Grok Bot infrastructure flaws let a malicious agent command lead to remote control and theft of connected-service credentials. The researchers say the weaknesses persisted after August disclosures to xAI and Cursor; the reports do not establish actual customer exploitation or the number exposed.
Israeli cyberattack-response firm Profero, founded in 2020, says flaws in Grok Bot, AI developer xAI’s service for carrying out tasks across applications, can turn a malicious agent command into remote administrative control of its working environment, according to the report describing its findings. The researchers say the weaknesses remained reproducible after more than two months of attempts to obtain a response from xAI and Cursor, which operates the agent’s sandbox infrastructure.
Grok Bot works with a computer in the cloud and signs into applications on a user’s behalf. In its August 11 launch announcement, xAI said the service grew from an internal prototype used for sales, marketing, operations and software work. The company explicitly described multiple bots sharing a computer and coordinating tasks.
That matters because the reported exposure encompasses the access users deliberately give the agent: browser sessions, working files and connections to email, calendars and other services. Profero’s claim is that a compromise of one agent can reach those resources across the same account.
At launch, Grok Bot was a beta available to SuperGrok, SuperGrok Plus and SuperGrok Heavy subscribers, as well as Cursor Pro, Pro+, Ultra and Teams Standard and Premium subscribers. xAI said its usage was separate from existing Grok and Cursor allowances; enterprise users could join a waitlist.
Profero helps organizations recover from cyberattacks. Its researchers are the source of the vulnerability and disclosure claims. The available coverage does not provide independent reproduction or vendor confirmation.
Cursor, whose product evolved from code completion into AI teammates, supplies the sandbox infrastructure, according to the reporting. The company said in its acquisition announcement that it had become part of SpaceX. Responsibility for investigating the reported chain therefore involves both the agent provider and its infrastructure operator.
A detailed account of Profero’s findings describes a path out of the sandbox—the environment intended to contain the agent’s activity. The reported attack starts with an attacker getting a malicious command executed inside an agent, potentially through content it encounters while working. The resulting infrastructure access is the critical second stage: an internal authentication token shared across environments and an unauthenticated container-management interface reportedly allow the attacker to gain administrative control of the virtual machine and issue commands remotely.
Ray-Ban’s US store cuts the Gen 2 Wayfarer by 25% to $284.25. Buyers still face separate prescription-lens prices, a cheaper Gen 1 option and newer glasses outside Meta’s frame sale.
This is a conditional attack chain. The reports do not demonstrate that an unauthenticated visitor can immediately take over an arbitrary customer’s account.
According to Profero, agents in the same account share one Linux user, filesystem and set of credentials. A successful compromise could therefore expose imported browser cookies, files the agent has worked on and tokens for connected services. The researchers say long-lived credentials also permit access to stored files and the insertion of new ones.
The same account describes an unauthenticated Chrome debugging interface, management traffic carrying replacement credentials without encryption, and an exposed private key used to sign a Cursor browser extension. The researchers reportedly used the key to sign a fabricated extension. That finding is distinct from evidence that attackers distributed such an extension to customers.
Profero says an intruder can intercept replacement credentials, undermining attempts to remove access simply by rotating them. Its description of a built-in “rootkit” refers to persistence using the product’s own components, without requiring an external malware implant.
The distinction from the ordinary chatbot matters too. A separate account of the research says the findings concern Grok Bot and its working environment, rather than necessarily applying to the regular Grok chat service.
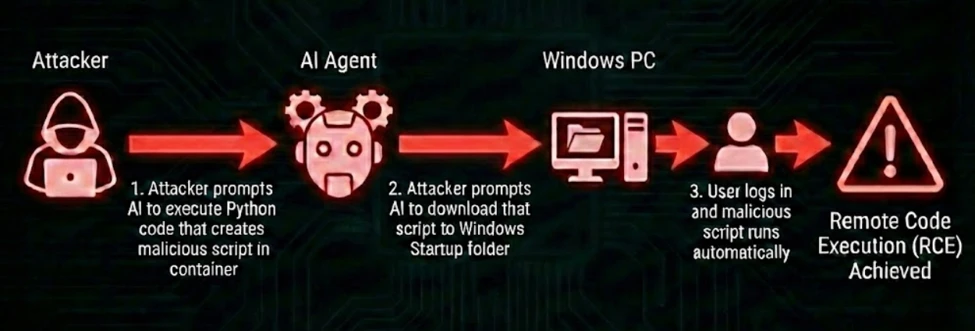
Microsoft’s company-reported Semantic Kernel attack chain illustrates vulnerabilities it says were fixed. It does not verify Profero’s Grok Bot findings. Source: Microsoft Security.
The general risk predates this disclosure. In its May 7 security research, Microsoft described two vulnerabilities in Semantic Kernel, its open-source framework for building AI agents and connecting models to applications. Microsoft said both had been fixed.
One path required an attacker to influence the agent’s input and the agent to use a particular search plugin configuration; another exposed a file-download function that could write a malicious file onto the host device. These were specific framework and tool defects. They neither verify the Grok Bot findings nor show that every agent deployment has the same exposure.
The useful comparison is the security boundary: model-generated tool calls can become real system actions, so the software handling those calls must constrain their permissions. In the Grok Bot case, the reported combination of shared account resources and reusable credentials makes the reach and persistence of a compromise central to the assessment.
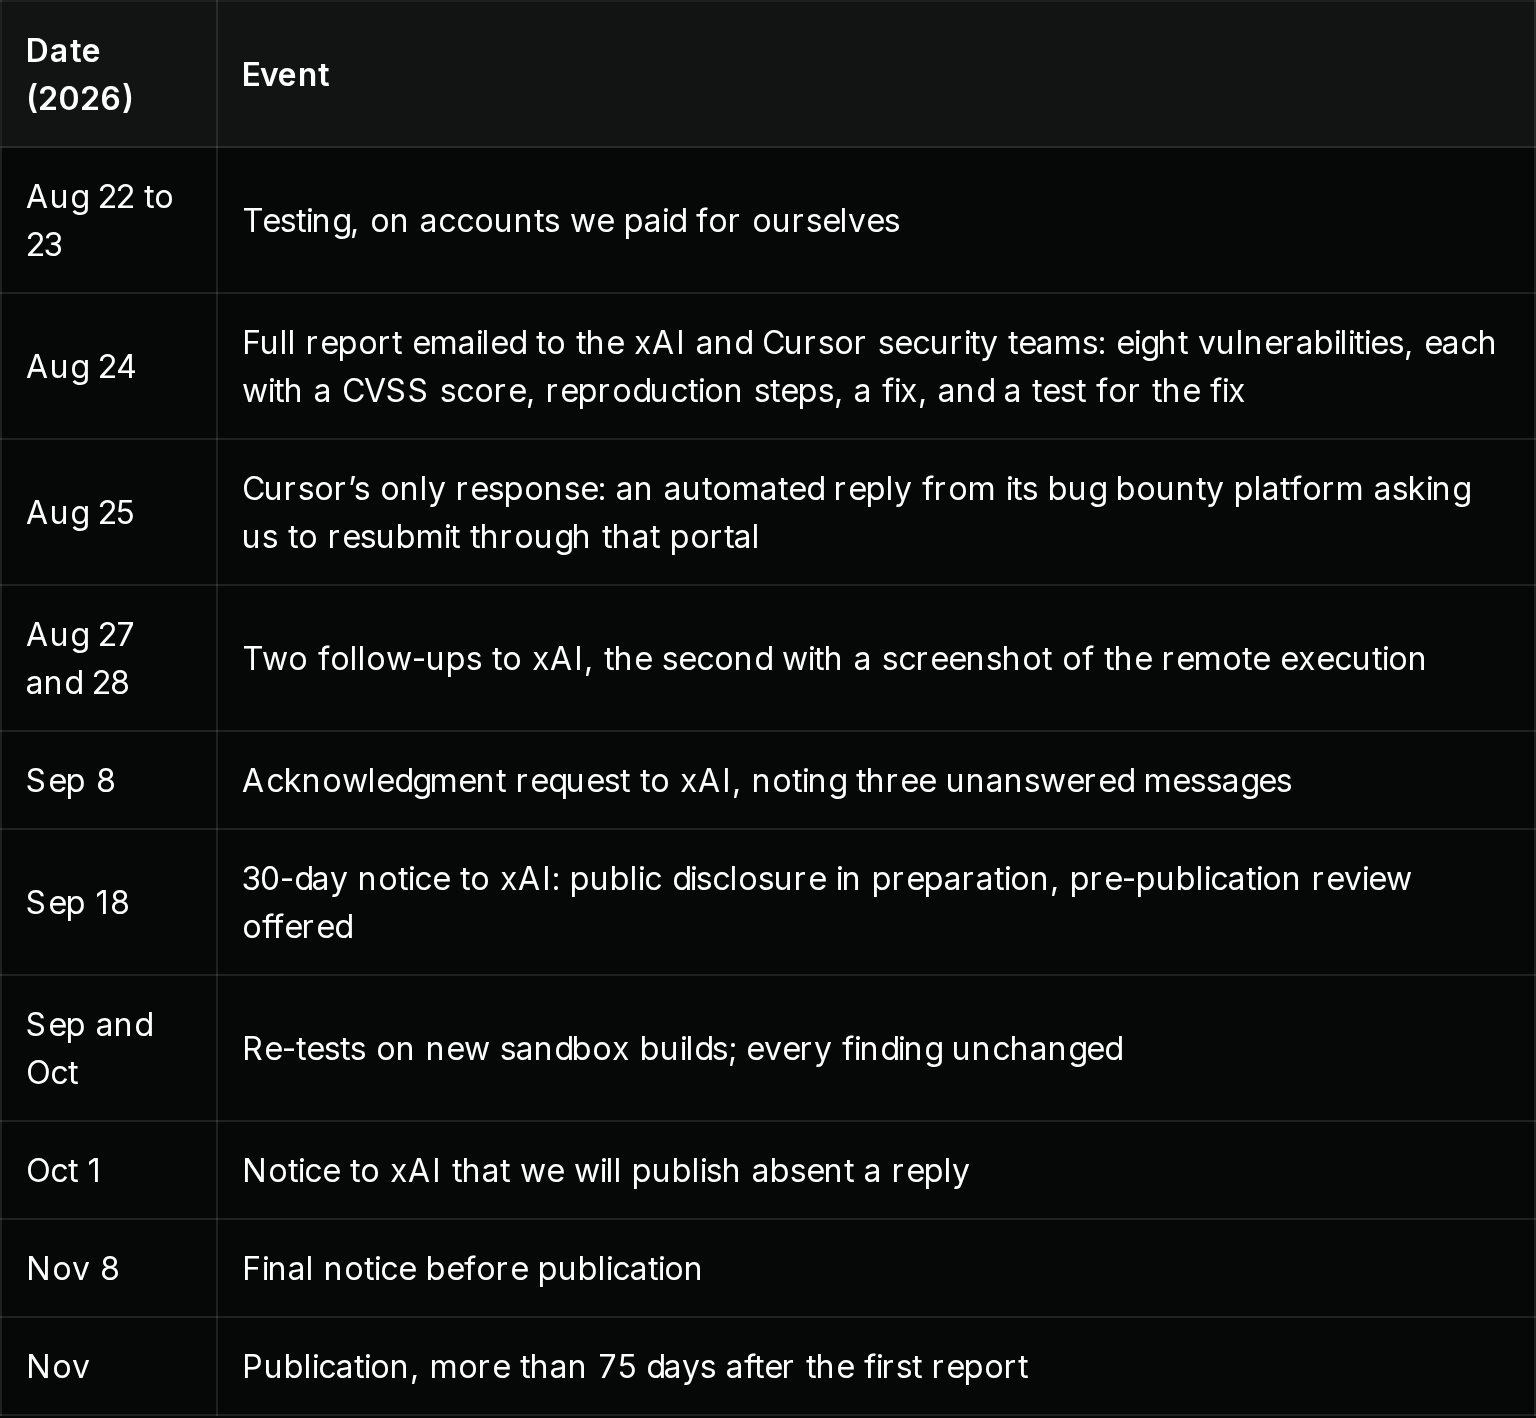
Profero’s company-reported disclosure chronology records its August 24 report, Cursor’s automated reply and subsequent follow-ups. Source: Profero.
Profero says it sent xAI and Cursor a detailed disclosure on August 24, covering eight vulnerabilities with severity scores, reproduction steps, proposed fixes and tests. Cursor sent an automated reply the next day directing the researchers to its bug-bounty portal. Profero says xAI did not answer repeated approaches and was notified on October 1 that publication would proceed without a response. The reports contain no substantive vendor answer.
Profero says repeated testing continued to reproduce the weaknesses. One report quotes Profero describing more than 240 problematic sandboxes it had built; others describe more than 240 software versions released since disclosure. Those are different measures, and neither is a count of affected users. Coverage differs on the vulnerability tally: two accounts describe eight, while the more detailed account refers to seven critical flaws. The available evidence does not reconcile those descriptions.
The next consequential evidence is a vendor account of which deployments are affected and reproducible tests showing that fixes block both initial control and renewed credential theft. Establishing whether anyone exploited the weaknesses would require a separate investigation of activity during the exposed period.
Ubisoft has made the team behind its Teammates experiment a dedicated subsidiary targeting AI characters with memory and outside game creators. Earlier playtests show both progress and limitations, while commercial plans remain undisclosed amid group cost cuts and refinancing.
Neuralink has shown a trial participant controlling GTA VI through intended movements. Earlier gaming use and company-reported trial results put the demonstration in context, while its reliability across users remains unmeasured in the reports.
SoftBank founder Masayoshi Son reportedly explored financing a $1 trillion acquisition of memory-chip maker SK hynix, but the company says the deal is no longer under active consideration. The target brings surging earnings, existing shareholders and customer commitments that complicate any simple equation between ownership and access to AI-memory supply.
Nvidia reported $115.8 billion in quarterly revenue, but its shares fell 14% Friday amid a wider technology selloff, a leadership transition and a reported accounting investigation. Strong cash generation offers a counterweight to concerns about the durability of AI spending.
The Nasdaq 100 fell 5.6% on November 20 and closed 19.8% below its record after an intraday bear-market breach. Nvidia’s revenue surge and Anthropic’s huge IPO did not halt the rout; infrastructure bills and resilience elsewhere in the market complicate the picture.
OpenAI reports sharply lower reasoning-extraction rates in internal GPT-6.2 tests and backs sanctions against illicit foreign distillation. Its own research and rival Anthropic’s experience show why protecting hidden reasoning leaves capability transfer and customer costs unresolved.
Alberta proposes 600-metre setbacks for large data centres and expanded utility oversight, but exemptions and rules still to be written will determine how much protection communities receive.
President Donald Trump backed Commerce Secretary Howard Lutnick as lawmakers scrutinize alleged delays in restricting a suspected route for AI chips to China. A new congressional inquiry also questions Nvidia’s influence on an existing investigation.

Amazon’s month-old Echo Time is $50 off for Black Friday. Its touchscreen, home hub and optional sleep-aware alarm cost $90 more than the reported Echo Spot price, while Alexa+ access and evidence of better waking remain key buying questions.
Merck will pair its experimental data with Isomorphic Labs’ AI to seek small-molecule cancer drug candidates. The deal follows Isomorphic’s $5 billion financing, but its payments, target and development timetable remain undisclosed.
Thinking Machines Lab released a roughly 20GB open-weights model that reuses its middle layers for reasoning. It brings the Inkling family to local hardware, with competitive coding results but workload-dependent costs and preliminary evidence on oversight.
Apple’s first HomePod mini update since 2020 adds Mac audio and four-speaker surround, but Siri AI remains unavailable, core home-hub features carry over, and reviews disagree on playback reliability.
Treasury Secretary Scott Bessent says an unnamed Anthropic founder will announce a large gift to children's investment accounts within weeks, but the amount, recipients and connection to existing philanthropic pledges remain undisclosed.
Google says air cooling will limit water use at its Visakhapatnam AI hub, but environmental proceedings and residents’ accounts raise broader questions about land, electricity, public incentives and the evidence behind promised benefits.
Nvidia slipped behind Alphabet to fourth in U.S. market value during November 20 trading. The reversal follows a steep selloff despite strong reported revenue growth, with a permanent CEO still to be chosen.
Google will close the Nest app on January 25, 2027 and retire Assistant on home speakers and displays in August. Device transfers are automatic, but continued voice access requires accepting Gemini; basic assistance remains free.

Amazon says Cairn agents exploited a MONAI Label zero-day to take over a university server. Other attacks failed, and maintainers list no patched package release.
Federal Reserve Governor Lisa D. Cook sees early AI pressure on coding, translation and young workers, but says a solid overall labor market and persistent inflation still call for tighter monetary policy.
President Donald Trump threatened a tax on U.S. companies building data centers abroad without specifying how it would work. The proposal raises questions for an AI export program that has received 78 applications and for domestic construction constrained by power and community opposition.