Editorial Team
4 min read
N-able says an intruder reached a server supporting Mail Assure and SpamExperts Hosted Cloud. Mail delivery and filtering continued, but customers lost management access as the company revoked tokens and worked to restore services securely.
N-able, a software provider serving managed service providers that operate IT systems for clients, says a cyberattack left users of its Mail Assure and SpamExperts Hosted Cloud email-security services without administrative access. Its status notice continued to report the portal and API offline at noon UTC on November 20, while saying mail delivery and filtering remained fully operational.
N-able lists the management portal, quarantine and logging among the unavailable services, with affected services across the Americas, Europe and Asia-Pacific. It says customers may be unable to view or release quarantined messages, review logs or change configurations, including adding or removing domains.
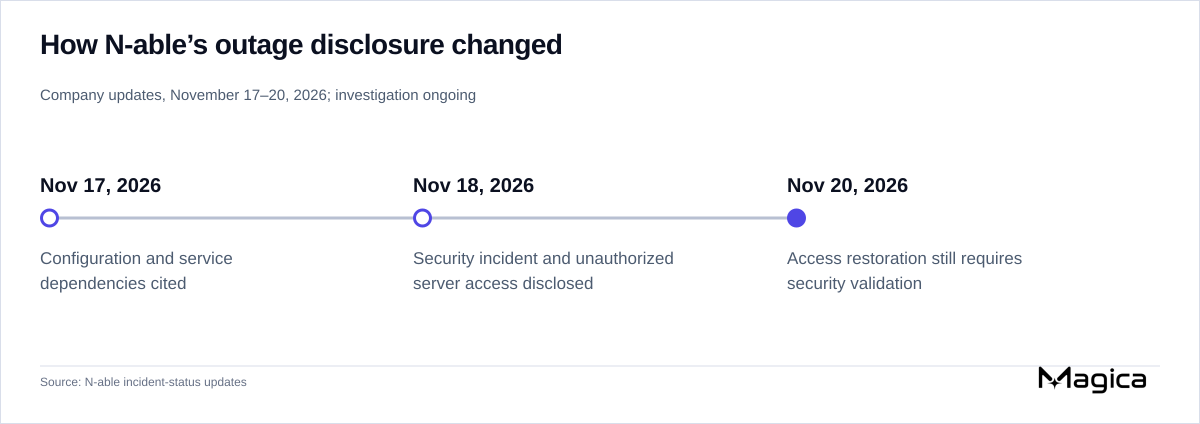
Company-reported updates from N-able trace its changing explanation and the security validation still required on November 20. Source: N-able.
N-able says it informed customers of a service disruption on November 16. It initially attributed the disruption to platform configuration and service dependencies; a November 17 update said remediation required rebuilding affected infrastructure and updating platform components. On November 18, it said further investigation had established a security incident and unauthorized server access. That notice also said the company had previously believed it had remediated the issue.
N-able said it identified the security incident on November 16 in an on-the-record statement carried in a report.
In a separate company statement reproduced in a report, N-able said its investigation had isolated the incident to a single web server, where an unauthorized party may have accessed stored credentials. It said it took that server offline, rotated internal platform credentials, revoked existing customer API tokens, invalidated OAuth tokens and proactively reset passwords for local users.
The management company supporting Japan's Shonan Beauty Clinic network disclosed stolen customer passwords stored without encryption and a separate booking-service incident. Treatment-related submissions were also exposed, while the affected population and financial impact remain under investigation.
N-able has said it has no evidence that customer data was compromised, including access to tenants’ mailboxes. That is the company’s assessment during an ongoing investigation; it does not resolve whether credentials were accessed. Revoking tokens and resetting passwords also does not establish that every credential covered by those measures was stolen.
The company says this incident is unrelated to the recent incident involving N-central, its remote monitoring and management platform. The separate N-central episode involved taking the platform offline while addressing disclosed vulnerabilities, according to the same report.
SolarWinds’ managed service provider business became the separate company N-able in July 2021. The email services’ roots go back further: SolarWinds MSP acquired SpamExperts in August 2017, adding a business launched in 2005 that offered inbound and outbound filtering and archiving to MSPs, internet service providers and telecommunications companies.
SpamExperts offered cloud and on-premises deployments; the current incident notices concern its Hosted Cloud service. The Mail Assure launch announcement that October explicitly included email continuity alongside filtering and archiving.
Supporting services undergoing restoration also include mailbox synchronization. The company’s claim that the intrusion was isolated to a single web server describes a different scope from the regional reach of the management disruption.
Recovery also extends to systems that connect through the disabled interfaces. The report carrying N-able’s statement warns that scripts and professional-services automation or billing integrations using revoked tokens will need attention once access returns. This is the report’s operational analysis, rather than a separate company finding about which integrations were affected.
In its November 20 noon update, N-able said development of remaining remediation measures was proceeding alongside testing, with each component required to pass security validation before access could be reinstated. It supplied no restoration deadline in that update, and its investigation remained ongoing.
The company says it has emailed partners information specific to their environments, including whether action is required. Partners who have not received that communication are directed to N-able Technical Support.
The outstanding questions are how the intruder entered, which credentials were accessible and whether the investigation changes the assessment of customer-data exposure. The available disclosures also do not establish an affected-customer count or a financial impact.
Microsoft is testing an optional Edge mode that blocks WebGL and WebGPU to reduce opportunities for browser exploitation. An early hands-on test found that restoring graphics for a trusted site also removed its broader Enhanced Security protections.
A critical authentication bypass gave a suspected China-linked espionage group access to VMware's virtualization control plane. Mandiant says the campaign stole signing keys and virtual-machine data, making compromise checks essential alongside patching.
PHP’s November 19 security releases address seven critical flaws, including unauthenticated code execution through reused backend connections. Patching takes priority, but applications that retain session upload progress must also check shared storage and serialization settings.
TfL has shut its Oyster photocard website after a breach that may have exposed around 265,000 customers’ account details, including security answers. Existing cards still work, while the attack method and restoration timetable remain undisclosed.
Around 40 Irish credit unions are implicated in a saved-payee data breach at software supplier Wellington IT. Missing logs leave the victim count unresolved, while a minister is seeking answers about the disclosure delay.
JPMorganChase says it believes attackers accessed marketing data at outside service providers, potentially exposing customer names and email addresses. The bank says services are unaffected, but has not identified the vendors or disclosed the attack date.
Apache confirms exploitation of a Roller code-execution flaw that survives disabling XML-RPC in its administration panel. Attacks on the retired Axis 1.x library also expose enterprise applications, making product-specific mitigation and compromise checks urgent.
StepSecurity’s Elephant-led Series A will fund broader protection for developer machines, package downloads and build pipelines, alongside planned defenses for AI-agent sandboxes. Its challenge is turning open-source adoption into a larger commercial platform while proving the extra controls earn their place.
Nvidia says it has found no indication its own systems were affected after The Gentlemen ransomware group listed it on a leak site. The investigation concerns a possible incident at a partner, while the gang has supplied no public proof.
Senators from both parties plan to delay the CISA nomination of Palantir security chief Michael LoSapio after his Jan. 6 denial, adding a confirmation obstacle as the agency faces staffing losses and funding decisions.
Sean Cairncross is leaving as national cyber director, with Pentagon CIO Kirsten A. Davies reportedly selected to succeed him. The transition puts Senate confirmation at the center of a cybersecurity leadership reshuffle.
Windows baseline protection combines existing PC safeguards into a verifiable pass-or-fail result. Microsoft defines the standard; developers choose whether failure means a warning, fewer features or blocked access.
F5 lists fixed releases for a critical nginx HTTP/2 flaw, while the wider NGINX2Root disclosure covers five independent nginx attack paths and a separate Linux kernel bug. Remediation depends on configuration, supplier patch levels and replacing vulnerable running processes.
Tyler Robert Buchanan received six years in U.S. prison for a phishing and SIM-swapping conspiracy that stole at least $11.6 million from individuals. He is the last of five defendants sentenced; restitution remains pending.
The new Threat Disruption Center makes TRM Labs its main technology partner following a reported $94.66 million sole-source award for Homeland Security Task Force investigations. A rival lost its court challenge, but the launch leaves the center’s share of that spending and its performance benchmarks undisclosed.
Fandango says payment details from certain October 8–11 transactions may have been exposed. State disclosures provide only a partial affected count, while the company has not explained how the checkout page was compromised.
Norway’s state-controlled oil and gas group is working to neutralise an attack on some IT systems. Employee services may be disrupted, but Equinor says operations and production remain unaffected and it has found no indications of data theft.
Tor urges relay operators to install 0.4.9.17 as a continuing DDoS attack strains its privacy network. A post-upgrade operator account describes further disruption, while Bitcoin connectivity measurements show partial recovery with important limits.
Malicious code in Optimizely website-testing projects could swap cryptocurrency addresses and skim payment cards. Optimizely says it has fixed the vulnerability and removed the code, but visitor exposure and losses remain unquantified.