Editorial Team
5 min read
Nvidia says it has found no indication its own systems were affected after The Gentlemen ransomware group listed it on a leak site. The investigation concerns a possible incident at a partner, while the gang has supplied no public proof.
Nvidia, the graphics processing unit maker whose business includes artificial intelligence and accelerated computing, says it is investigating an incident that may have affected a third-party partner after The Gentlemen ransomware operation claimed it as a victim. The distinction leaves two questions open: whether Nvidia-related data was stolen from a partner, and whether the gang can substantiate its claim at all.
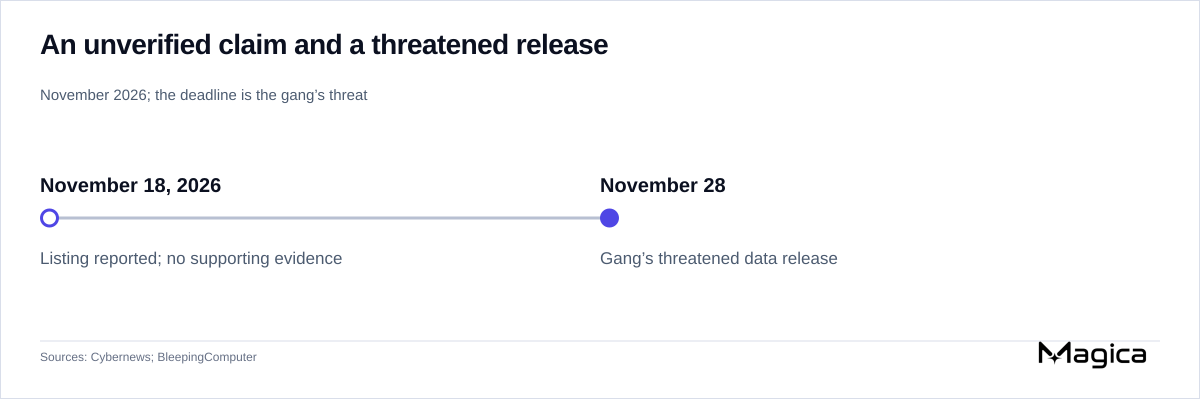
The listing was reported without supporting samples. November 28 is the gang’s threatened release date, not evidence that data was stolen. Source: Cybernews.
The listing was spotted on November 18. It promised information about the alleged data later, but contained no samples. Nvidia subsequently said it was investigating an incident that may have affected a third-party partner, according to the report carrying its response.
A company spokesperson said in a separate response:
“We have found no indication that NVIDIA systems or networks were affected. We continue to monitor the situation.”
That distinction matters: data associated with a company can be exposed through a supplier without attackers entering the company’s own network. Nvidia’s statement leaves a possible partner incident under investigation; it does not confirm the gang’s account of what it obtained.
The gang’s countdown points to November 28. Its post did not identify the allegedly compromised business unit or explain when an intrusion occurred, according to the description of the listing. No public ransom amount or data volume is established in the available reporting.
The management company supporting Japan's Shonan Beauty Clinic network disclosed stolen customer passwords stored without encryption and a separate booking-service incident. Treatment-related submissions were also exposed, while the affected population and financial impact remain under investigation.
The same leak site also lists Taiwan-based Jentech Precision Industrial, which describes itself as an Nvidia partner for AI data-center cooling. Jentech did not immediately respond to a request for comment in the report identifying that connection. Neither that listing nor the commercial relationship establishes that Jentech is the partner Nvidia is investigating.
Nvidia has previously distinguished partner exposure from a compromise of its own services. In May 2026, it confirmed that a hack of a regional GeForce NOW Alliance partner exposed information belonging to some Armenian users, including contact details, dates of birth and usernames. Nvidia said its network and Nvidia-operated services were unaffected, according to the account of that earlier incident.
The same account describes a direct breach disclosed in March 2022, claimed by the Lapsus$ extortion gang, that affected more than 71,000 employees after attackers accessed Nvidia’s network the previous month. These are distinct precedents, not evidence of the current claim’s scope.
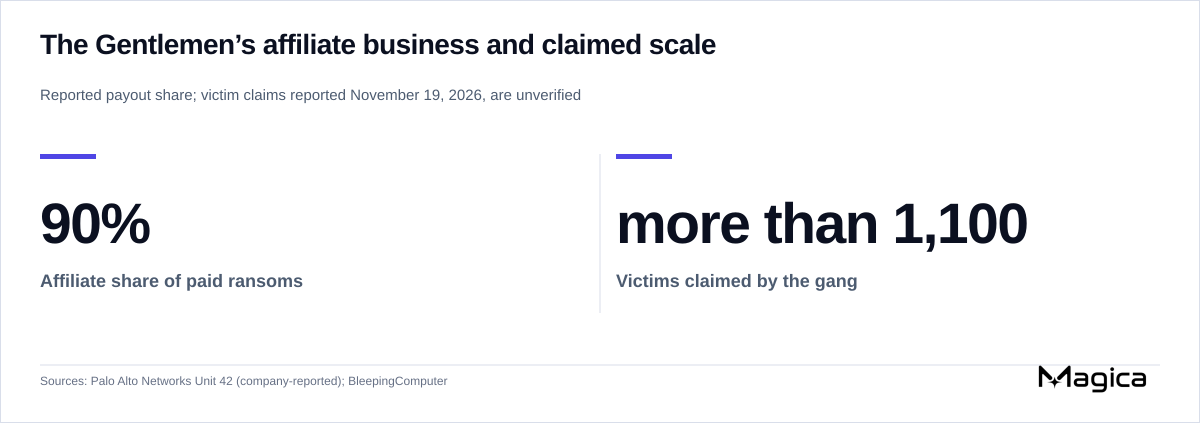
Unit 42’s company-reported analysis describes a 90% affiliate payout. More than 1,100 claimed victims were reported on November 19; these are not independently confirmed breaches. Source: Palo Alto Networks Unit 42.
The Gentlemen supplies ransomware to affiliates that conduct attacks for a share of payments. Palo Alto Networks’ threat-research group Unit 42 dates its activity to at least July 2025. Its July 2026 analysis, drawing on earlier public research, says the operators likely previously worked as ArmCorp, an affiliate of the Qilin ransomware service, before moving from a private operation to an affiliate model around September 2025.
That history helps explain how the operation scales. Unit 42 cites research putting its affiliate payout at 90% of paid ransoms, against a typical 70%–80% for other ransomware services. The comparison concerns the division of ransom proceeds, not the size of payments or verified revenue. The gang combines data theft with encryption and threats to publish stolen information.
Unit 42 and other researchers have observed access methods including exploiting vulnerable firewalls and VPNs, using stolen credentials and working with brokers that sell network access. Those findings describe the gang’s broader operations; they do not establish an entry method or encryption in the Nvidia case.
The gang has claimed more than 1,100 victims across multiple industries, according to the November account of its track record. These are claims, not independently confirmed breaches.
Cybernews security researcher Aras Nazarovas warned in his assessment of the Nvidia listing that the group had previously exaggerated claims, misattributed companies and reused stolen data. His warning supports checking the files and their origin; it does not establish that this claim is false or inconsequential.
The next meaningful evidence would identify the affected partner and authenticate any alleged files, including where they originated and whose information they contain. The available reporting establishes neither the volume nor the sensitivity of any data involved, and provides no basis to conclude that Nvidia’s systems were encrypted.
The November 28 deadline is the gang’s publication threat. A substantive update from Nvidia or the affected partner, together with authenticated evidence of access, would help distinguish a partner exposure from a direct compromise or an unsupported claim. Until then, neither a confirmed Nvidia breach nor an all-clear for partner-held data follows from the available evidence.
N-able says an intruder reached a server supporting Mail Assure and SpamExperts Hosted Cloud. Mail delivery and filtering continued, but customers lost management access as the company revoked tokens and worked to restore services securely.
Microsoft is testing an optional Edge mode that blocks WebGL and WebGPU to reduce opportunities for browser exploitation. An early hands-on test found that restoring graphics for a trusted site also removed its broader Enhanced Security protections.
A critical authentication bypass gave a suspected China-linked espionage group access to VMware's virtualization control plane. Mandiant says the campaign stole signing keys and virtual-machine data, making compromise checks essential alongside patching.
PHP’s November 19 security releases address seven critical flaws, including unauthenticated code execution through reused backend connections. Patching takes priority, but applications that retain session upload progress must also check shared storage and serialization settings.
TfL has shut its Oyster photocard website after a breach that may have exposed around 265,000 customers’ account details, including security answers. Existing cards still work, while the attack method and restoration timetable remain undisclosed.
Around 40 Irish credit unions are implicated in a saved-payee data breach at software supplier Wellington IT. Missing logs leave the victim count unresolved, while a minister is seeking answers about the disclosure delay.
JPMorganChase says it believes attackers accessed marketing data at outside service providers, potentially exposing customer names and email addresses. The bank says services are unaffected, but has not identified the vendors or disclosed the attack date.
Apache confirms exploitation of a Roller code-execution flaw that survives disabling XML-RPC in its administration panel. Attacks on the retired Axis 1.x library also expose enterprise applications, making product-specific mitigation and compromise checks urgent.
StepSecurity’s Elephant-led Series A will fund broader protection for developer machines, package downloads and build pipelines, alongside planned defenses for AI-agent sandboxes. Its challenge is turning open-source adoption into a larger commercial platform while proving the extra controls earn their place.
Senators from both parties plan to delay the CISA nomination of Palantir security chief Michael LoSapio after his Jan. 6 denial, adding a confirmation obstacle as the agency faces staffing losses and funding decisions.
Sean Cairncross is leaving as national cyber director, with Pentagon CIO Kirsten A. Davies reportedly selected to succeed him. The transition puts Senate confirmation at the center of a cybersecurity leadership reshuffle.
Windows baseline protection combines existing PC safeguards into a verifiable pass-or-fail result. Microsoft defines the standard; developers choose whether failure means a warning, fewer features or blocked access.
F5 lists fixed releases for a critical nginx HTTP/2 flaw, while the wider NGINX2Root disclosure covers five independent nginx attack paths and a separate Linux kernel bug. Remediation depends on configuration, supplier patch levels and replacing vulnerable running processes.
Tyler Robert Buchanan received six years in U.S. prison for a phishing and SIM-swapping conspiracy that stole at least $11.6 million from individuals. He is the last of five defendants sentenced; restitution remains pending.
The new Threat Disruption Center makes TRM Labs its main technology partner following a reported $94.66 million sole-source award for Homeland Security Task Force investigations. A rival lost its court challenge, but the launch leaves the center’s share of that spending and its performance benchmarks undisclosed.
Fandango says payment details from certain October 8–11 transactions may have been exposed. State disclosures provide only a partial affected count, while the company has not explained how the checkout page was compromised.
Norway’s state-controlled oil and gas group is working to neutralise an attack on some IT systems. Employee services may be disrupted, but Equinor says operations and production remain unaffected and it has found no indications of data theft.
Tor urges relay operators to install 0.4.9.17 as a continuing DDoS attack strains its privacy network. A post-upgrade operator account describes further disruption, while Bitcoin connectivity measurements show partial recovery with important limits.
Malicious code in Optimizely website-testing projects could swap cryptocurrency addresses and skim payment cards. Optimizely says it has fixed the vulnerability and removed the code, but visitor exposure and losses remain unquantified.